Dependabot-based dependency graphs for Python
Python projects will now see more complete and accurate transitive dependency trees in their dependency graphs and Software Bills of Materials (SBOMs). This feature is based on a new type…
Python projects will now see more complete and accurate transitive dependency trees in their dependency graphs and Software Bills of Materials (SBOMs). This feature is based on a new type…
We are migrating the download URLs for Copilot usage metrics reports from Azure Front Door domains to a stable, GitHub-owned custom domain. This change will improve URL stability and make…
CodeQL is the static analysis engine behind GitHub code scanning, which finds and remediates security issues in your code. You can now define custom sanitizers and validators using data extensions…
Agent skills are reshaping how developers work with AI coding agents. Today we’re launching gh skill, a new command in the GitHub CLI that makes it easy to discover, install,…
CodeQL is the static analysis engine behind GitHub code scanning, which finds and remediates security issues in your code. We’ve recently released CodeQL 2.25.2, which brings a new Kotlin version…
We’re sharing recent policy updates that developers should know about, updating our Transparency Center with the full year of 2025 data, and looking to what’s ahead.
Dependabot and code scanning now support OpenID Connect (OIDC) authentication for private registries configured at the organization level, eliminating the need to store long-lived credentials as repository secrets. What’s new…
Artifact and deployment context now appears in two new places: repository properties and security alert pages. Repository properties: deployable and deployed Two new built-in repository properties—deployable and deployed—are now available.…
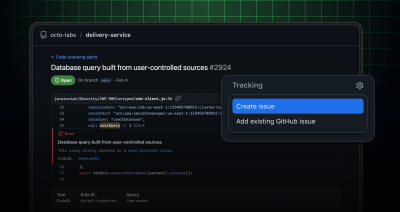
You can now link code scanning alerts to GitHub Issues, bringing security remediation into your existing planning and tracking workflows. This functionality is in public preview. With this update, you…
It’s now easier to configure Dependabot and code scanning for organizations that rely on multiple internal package feeds. Previously, organization-level settings only allowed a single private registry configuration per ecosystem…
This week, we’re rolling out several improvements to our detection coverage, APIs, and workflows. These improvements strengthen our continued investment in the developer experience of our secret scanning features. Built…
The new Code Security Risk Assessment gives you a one-click view of vulnerabilities across your organization, at no cost.
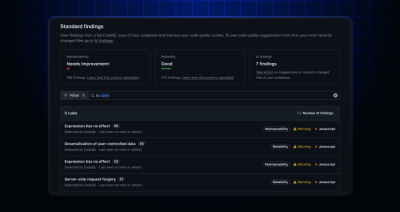
We’ve updated the GitHub Code Quality experience to make it easier to navigate and triage findings across your repository. GitHub Code Quality standard findings help you detect potential reliability and…
Learn how to create a free website for any repository on GitHub Pages.
When Copilot cloud agent writes code, it automatically runs GitHub’s security and quality validation tools, including CodeQL, the GitHub Advisory Database, secret scanning, and Copilot code review. If any problems…
This week, we’re rolling out several improvements to our APIs, webhooks, and delegated workflows. These improvements strengthen our continued investment in the developer experience of our secret scanning features. Built…
Get inspired by five of the most memorable, magical, and quirky Universe sessions to date.
Some dependency vulnerabilities require more than a version bump—they need code changes across your project. Now generally available, you can assign Dependabot alerts to AI coding agents, including Copilot, Claude,…
Dependabot now supports Nix flakes. Add nix as a package ecosystem in your dependabot.yml file. Dependabot will then monitor your flake.lock inputs and open pull requests when newer commits are…
npm trusted publishing now supports CircleCI as an OIDC provider, joining GitHub Actions and GitLab CI/CD. Maintainers publishing from CircleCI workflows can now eliminate stored credentials entirely and authenticate directly…
Editor’s note (April 20, 2026): We updated this post to clarify in preview, VNET failover manual and not automated This month, GitHub Actions adds entrypoint and command overrides for service…

Build what’s next on GitHub, the place for anyone from anywhere to build anything.

Catch up on the key announcements shaping the future of software development.

