How we took malware advisories beyond npm
GitHub malware advisories no longer stop at npm. Here’s how we wired OpenSSF’s malicious-packages data into the Advisory Database, and why we built the pipeline paranoid.
GitHub malware advisories no longer stop at npm. Here’s how we wired OpenSSF’s malicious-packages data into the Advisory Database, and why we built the pipeline paranoid.

Enterprise administrators can now customize managed settings by targeting enterprise teams with itemized configuration files. Large enterprises can scale governance without bottlenecking every configuration change through central administrators or one-size-fits-all…
Dependabot keeps your dependencies current, but its defaults can flood your repository with pull requests. Here’s how grouping updates, slowing the cadence, and keeping security fixes fast cut the noise on a Microsoft open source project.
Explore the changes we’ve shipped across npm and GitHub Actions over the past few months to disrupt supply chain attack techniques and limit their impact.
A new default three-day cooldown delays version update pull requests so maintainers and security researchers can address findings in a release before it gets into your code.
Celebrating $100 million contributed by the community to the people who build and sustain open source every day.
Dependabot now waits until a new release has been available on its registry for at least three days before opening a version update pull request. This cooldown is now the…
Explore how the Aspire team turns merged product changes into SME-reviewed docs pull requests, closing the gap between release and documentation.
GitHub Enterprise Cloud customers with enterprise managed users can now access GitHub Copilot agent session data across all Copilot clients, including: Cloud agents operating on github.com and data resident deployments…
Explore how the Open Source Program Office uses GitHub’s new license compliance product to manage open source dependencies at scale.
The GitHub Advisory Database is processing more vulnerability reports than ever before. Here’s what’s driving the surge, how we’re responding, and how the community can help.
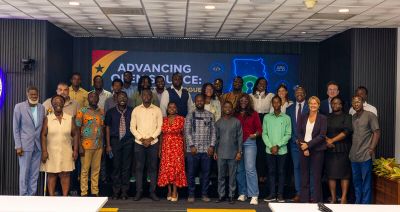
GitHub joined the United Nations Development Programme in Ghana to explore how open source governance can support one of West Africa’s most ambitious digital reform efforts.
We’re calling for targeted amendments to resolve conflicts with open source licensing and align with international transparency frameworks while preserving regulatory intent.
Learn how pull request limits can help manage contribution volume in your repositories, and see what’s next on the roadmap.
Editor’s note (July 15, 2026): We updated this post to reflect a revised backport enforcement date. Enforcement for backported versions of actions/checkout has been moved from July 16, 2026 to…
Custom agents let GitHub Copilot CLI understand your stack and team workflows, turning one-off terminal prompts into repeatable, reviewable processes.
At Microsoft Build 2026, GitHub introduced new tools, updates, and surfaces so agents can work the way you already work.
We are committed to empowering every developer by building an open, secure, and AI-powered platform that defines the future of software development.
Following our previous updates, GitHub Copilot for Eclipse is open source, with the code available on GitHub under the MIT license. This marks an important milestone for GitHub Copilot in…
Check out these 10 open source tools that help game developers create art, animation, levels, audio, dialogue, debug UIs, and engine-ready assets.
GitHub Enterprise Server customers need to take immediate action.

Build what’s next on GitHub, the place for anyone from anywhere to build anything.

Join us October 28-29 in San Francisco or online for GitHub Universe, our flagship developer event uniting people, agents, and the world’s code.

