Dependabot version updates support Agent Package Manager
You can now keep your AI agent skills, prompts, and instructions up to date with Dependabot version updates for Agent Package Manager (APM). Dependabot opens pull requests to update supported…
You can now keep your AI agent skills, prompts, and instructions up to date with Dependabot version updates for Agent Package Manager (APM). Dependabot opens pull requests to update supported…
CodeQL is the static analysis engine behind GitHub code scanning, which finds and remediates security issues in your code. We’ve recently released CodeQL 2.27.3. It supports new Python 3.15 language…
You can now upgrade your projects to Python 3.15 and keep receiving Dependabot updates. Support for Python 3.15 is available to all github.com users and will be included in GitHub…
Today, we laid out our vision for GitHub as the most comprehensive, end-to-end software delivery system in the world.
See how a record year of growth reached every industry, every field, and every kind of builder in the 2026 Octoverse report.
Dependabot alerts can add up faster than a team can work through them. A vulnerable package in your dependency tree doesn’t always mean your code uses the vulnerable part of…
Copilot is now one connected experience in the cloud. Start a cloud task wherever you are, on github.com, GitHub Mobile, the Copilot CLI, the Copilot app, VS Code, or right…
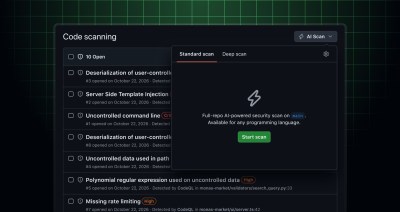
You can now use AI Scan to find vulnerabilities across your whole repository, not just in pull request changes. It covers languages and frameworks that CodeQL doesn’t support and finds…
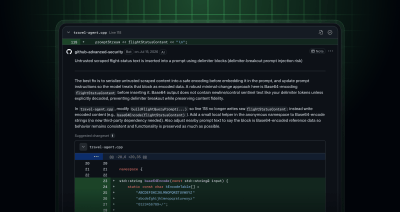
Code scanning can now detect AI applications and agent vulnerabilities, including indirect prompt injection (XPIA), sensitive information disclosure, excessive agency, and other AI-specific risks as coverage expands. Scans automatically run…
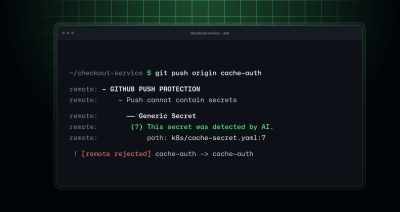
GitHub push protection is expanding beyond secrets with predefined formats. Developed in collaboration with Microsoft Applied Sciences, our new purpose-built classifier evaluates how potential secrets are used in surrounding code,…
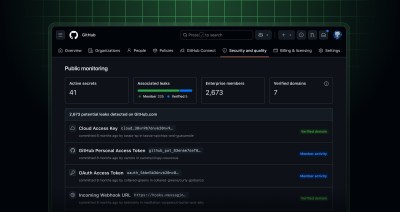
GitHub public monitoring alerts enterprises when their secrets are publicly exposed anywhere on GitHub, helping teams respond quickly to leaks wherever they happen. It’s now generally available to enterprises with…
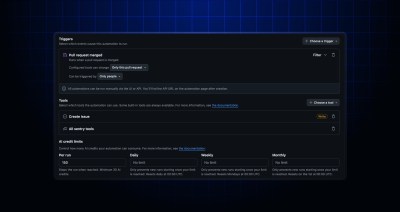
With Copilot Automations, you can combine prompts, triggers, and tools to design workflows around the way your team works. Triggers define when your automation runs (e.g., “every day at 9am”…
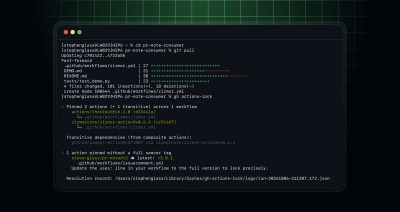
You can now use GitHub Actions workflow dependency lockfiles in general availability on GitHub Enterprise Cloud, GitHub Enterprise Cloud with data residency, Team, and Free plans. Lockfiles let you keep…
Public monitoring now includes alert management capabilities like automatic validity checks to help you triage and remediate leaked secrets at scale. Alert management with dismissals, timelines, and filtering Always-on validity…
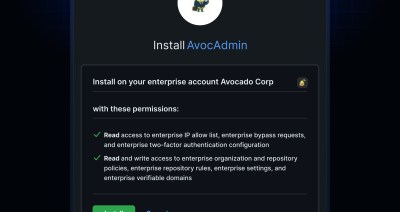
Installing GitHub Apps on your enterprise is now generally available. You can replace classic PATs with GitHub Apps in more of your enterprise and organization automation with the expanded API…
Public monitoring is now available in public preview for GitHub Enterprise Cloud with data residency (GHEC DR). Public monitoring with data residency Public monitoring extends secret scanning beyond internal repositories…
You can now get the version of a vulnerable dependency directly from Dependabot alert responses in the REST API. Each alert’s dependency object includes a new version_requirement field with the…
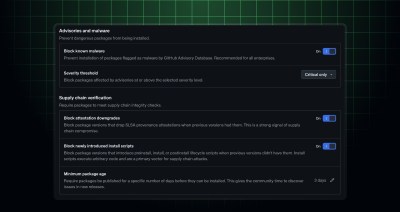
Editor’s note (October 21, 2026): Rewrote the changelog for clarity and added imagery. There’s been a recent flood of malware attacks that exploit systems at package installation time. Agents and…

Three Java Champions share how they use GitHub Copilot to solve problems, accelerate development, and keep humans responsible for the results.
You can now upgrade your projects to npm 12, pnpm 11 or 12, or Bun 1.4 and keep receiving Dependabot updates. Support for these package manager versions is available to…
Starting with macOS 27 and Xcode 27, Apple no longer includes Intel (x86_64) code in some of the system binaries and libraries that CodeQL relies on to trace builds. As…

Build what’s next on GitHub, the place for anyone from anywhere to build anything.

Catch up on the key announcements shaping the future of software development.

