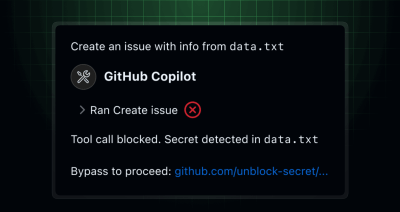
GitHub MCP Server: Secret scanning, push protection, and more
The remote GitHub MCP server now scans all of its tool call inputs in public repositories. If an exposed secret is detected, the call is blocked by default with clear…
The remote GitHub MCP server now scans all of its tool call inputs in public repositories. If an exposed secret is detected, the call is blocked by default with clear…
Learn how the International Telecommunication Union made the switch to open source, and how you can too!
Secret scanning is adding validity check support for 12 additional token types across 11 providers. In addition to previously announced token types, you will now see validity checks for the…
Dependabot now supports automatic dependency updates for vcpkg, the free C/C++ package manager from Microsoft. This enables teams using vcpkg to keep their C and C++ dependencies secure and up-to-date…
Learn how the GitHub Secure Open Source Fund helped 71 open source projects significantly improve their security posture through direct funding, expert guidance, and actionable playbooks.
tl;dr: I am stepping down as GitHub CEO to build my next adventure. GitHub is thriving and has a bright future ahead. The following is the internal post I sent to GitHub employees (Hubbers) this morning announcing my departure.
GitHub continually updates the default pattern set for secret scanning with new patterns and upgrades to existing patterns, helping ensure your repositories have comprehensive detection for different secret types. The…
Learn how to integrate AI features with GitHub Models directly in GitHub Actions workflows.
As of today, npm trusted publishing with OpenID Connect (OIDC) is now generally available. This feature enables you to securely publish npm packages directly from CI/CD workflows using OpenID Connect…

Upgrade from a local MCP Docker image to GitHub’s hosted server and automate pull requests, continuous integration, and security triage in minutes — no tokens required.
On July 28, 2025 21:41 UTC, GitHub Enterprise Importer (GEI) was identified as being in a degraded state with migrations stalled. An incident was declared to restore the service to…
What’s new You can now dismiss or reopen multiple Dependabot alerts at once across your entire organization, making alert management more efficient for security and development teams. Previously, organization-level alert…
We’re investing in keeping Dependabot relevant for modern development teams, whether you’re experimenting with a new language or relying on the latest version of your favorite package manager. We’ve expanded…
Secret scanning is adding validity check support for eight additional token types across five providers. In addition to previously announced token types, you will now see validity checks for the…
More context can mean more attack surfaces for your projects. Be prepared for what lies ahead with this guide.

Build a custom Azure DevOps extension that eliminates the complexity of JWT generation and token management, enabling powerful automation and enhanced security controls.
Open source software is critical infrastructure, but it’s underfunded. With a new feasibility study, GitHub’s developer policy team is building a coalition of policymakers and industry to close the maintenance funding gap.
Secret scanning is adding validity check support for 45 additional token types across over 30 providers. What’s changing? In addition to previously announced token types, you will now see validity…
Organization administrators can now centrally configure private registries for Dependabot at the organization level, streamlining dependency management across all repositories. What’s new Previously, organizations had to individually configure private registry…
Starting on July 22nd, 2025, GitHub code scanning will no longer combine multiple SARIF files that share the same tool and category properties. Impacted SARIF files will also be rejected.…
Strengthen your repositories against actions workflow injections — one of the most common vulnerabilities.

Build what’s next on GitHub, the place for anyone from anywhere to build anything.

Catch up on the key announcements shaping the future of software development.

