GitHub Rebase #14
Want to get on Rebase? Find out how. Stats Breakdown Featured Project dynomite is an open-source Erlang implementation of Amazon’s Dynamo, a distributed key-data storage that strives for high availability.…
Want to get on Rebase? Find out how. Stats Breakdown Featured Project dynomite is an open-source Erlang implementation of Amazon’s Dynamo, a distributed key-data storage that strives for high availability.…
Featured Project visor adds a system-wide hotkey that can bring up your terminal, much like games that allow instant access to developer console to tweak settings and run commands. Based…
And we’re back! Rebase went on a bit of hiatus, but it has returned in full force for 2009. Read on for the latest and greatest coming out of GitHub!…

Discover how the Ersilia Open Source Initiative accelerates drug discovery by using GitHub Actions to disseminate AI/ML models.
Generate and verify signed attestations for anything you make with GitHub Actions.
Some best practices and important defenses to prevent common attacks against GitHub Actions that are enabled by stolen personal access tokens, compromised accounts, or compromised GitHub sessions.

With enterprise accounts for all, your organization can take advantage of all that GitHub Enterprise has to offer, from GitHub Actions and GitHub Advanced Security, to Copilot.

The Sigstore GA means you can protect your software supply chain today with GitHub Actions, and will power new npm security capabilities in the near future.

GitHub Actions workflows in the Security category will now appear among the workflow recommendations based on a repository’s content.
You can now use the generally available Xcode 27 runner image to build and test your Apple applications in GitHub Actions. Previously in public preview, this GitHub-hosted image runs on…
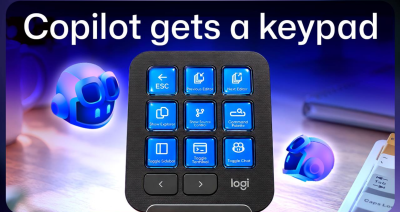
AI, agents, voice, and physical controls are shifting software development from operating tools to expressing intent—and helping developers stay focused on building.
Put native GitHub features to work to review outside collaborator access and archive stale repositories.
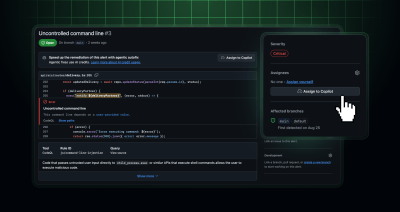
Agentic autofix for code scanning alerts is now generally available. It remediates alerts by working across your codebase the way a developer would: it explores relevant files, proposes a fix,…
As of October 15, 2026, email notifications for repository push events have been retired and are no longer sent. We shut down this feature to help prevent spam and abuse.…
CodeQL 2.27.2 is now available, adding a C++ regular-expression parser and analysis improvements across several languages. CodeQL is the static analysis engine behind GitHub code scanning, which helps you find…
We’re rebuilding GitHub’s Git infrastructure while GitHub keeps running, creating a foundation for agent-scale software development.
Unvalidated npm trusted publishing configurations now expire 48 hours after creation and can no longer authorize publishing. This limits the risk of trusting a repository or project name that changes…
The enforcement date for GitHub Actions minimum version requirements for self-hosted runners on GitHub Enterprise Cloud has changed. The change ships Monday, September 28, 2026, and full enforcement now begins…
CodeQL 2.27.1 adds new queries for C/C++ and C#, support for Kotlin 2.4.20, and query-accuracy improvements. CodeQL is the static analysis engine behind GitHub code scanning, which helps you find…
The Ubuntu 26.04 runner image for GitHub Actions is now out of public preview and fully supported for production workflows on both x64 and arm64. As part of this release,…
CodeQL 2.27.0 is now available on Linux ARM64, adds a new Rust security query, expanded framework coverage for Java/Kotlin and C#, and analysis accuracy improvements across multiple languages. CodeQL is…

Build what’s next on GitHub, the place for anyone from anywhere to build anything.

Join us October 28-29 in San Francisco or online for GitHub Universe, our flagship developer event uniting people, agents, and the world’s code.

